Set up SSO with Microsoft Entra ID
Step-by-step Microsoft Entra ID (Azure AD) setup for Clevera single sign-on, with SAML 2.0 or OpenID Connect: the enterprise app or app registration, signing, claims, which values go where, and testing.
Set up single sign-on between Microsoft Entra ID (formerly Azure AD) and Clevera so your team signs in with their Microsoft work account. You can connect with SAML 2.0 or OpenID Connect (OIDC); this guide covers both on the Entra side and the matching fields in Clevera.
The Microsoft Entra admin center changes from time to time. If a label below doesn't match, look for the setting with the same meaning, and use the general guides for the full list of values: SAML, OIDC.
Before you start
- You're the owner of a Clevera workspace on a Custom plan.
- You can create enterprise applications or app registrations in Entra (for example as an Application Administrator).
- You know the email domains your people use, such as
acme.example.
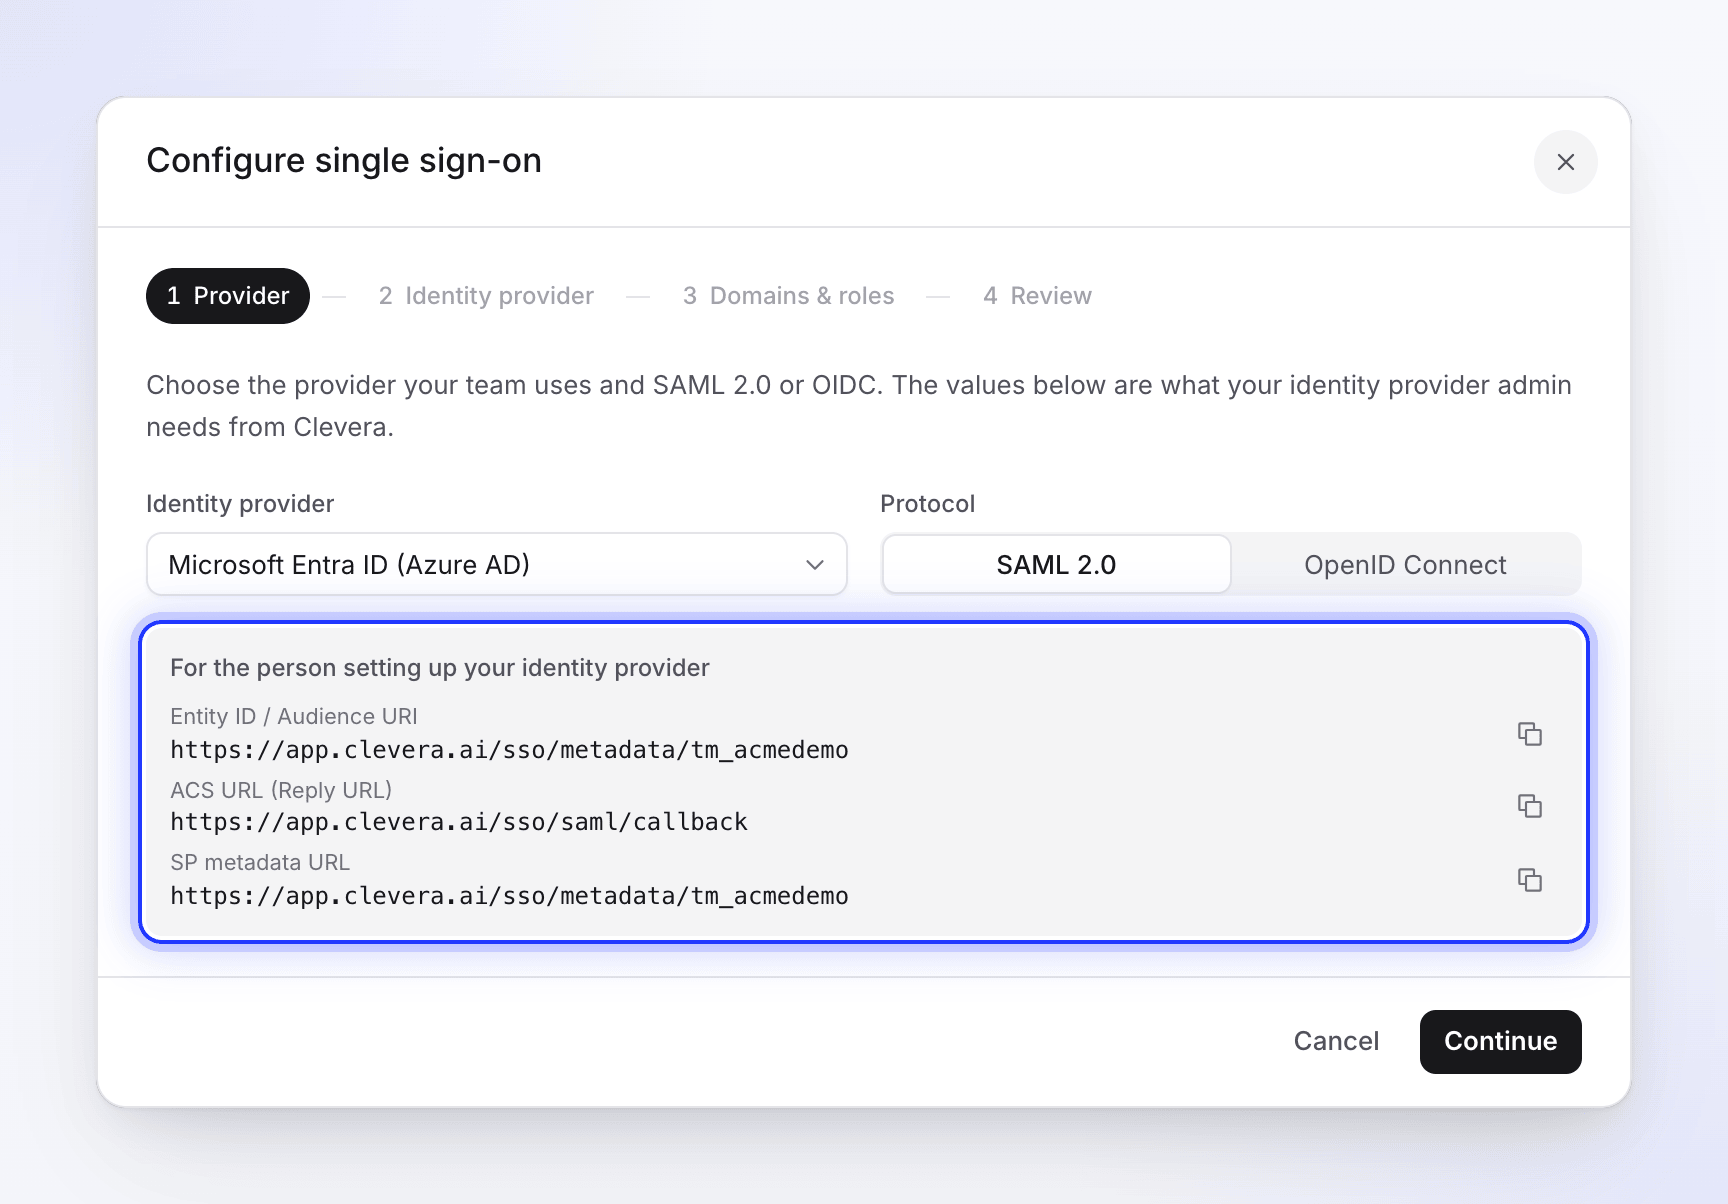
Open the Clevera setup dialog first, so you can copy values from it: open the workspace menu at the top of the sidebar, choose Team settings, then Security, and click Set up SSO. Choose Microsoft Entra ID (Azure AD) as the Identity provider.
Connect with SAML 2.0
Create an enterprise application
In the Microsoft Entra admin center, go to Enterprise applications and click New application, then Create your own application. Name it
Clevera, choose Integrate any other application you don't find in the gallery (Non-gallery) and click Create.Choose SAML
In the new app, open Single sign-on and choose SAML.
Enter Clevera's values
In Basic SAML Configuration, click Edit and fill in:
Entra field Value from Clevera Identifier (Entity ID) Entity ID / Audience URI (copy it from the Clevera dialog; it ends in your workspace ID) Reply URL (Assertion Consumer Service URL) https://app.clevera.ai/sso/saml/callbackSign on URL Leave empty Relay State Leave empty Logout Url Only if you'll use single logout: https://app.clevera.ai/sso/saml/sloClick Save.
Check the claims
In Attributes & Claims, open Unique User Identifier (Name ID). Set Name identifier format to Email address and the source attribute to the attribute that holds people's email:
user.mail, oruser.userprincipalnameif their sign-in name is their email. Keep the defaultgivenname,surnameandemailaddressclaims: Clevera reads them.Sign the response and the assertion
In SAML Certificates, click Edit next to the signing certificate. Set Signing Option to Sign SAML response and assertion and Signing Algorithm to SHA-256. Click Save.
Entra signs only the assertion by default, and Clevera rejects that.
Copy Entra's values into Clevera
In SAML Certificates, download Certificate (Base64) and open it in a text editor. In Set up Clevera, copy the URLs. In Clevera, set Protocol to SAML 2.0, click Continue, and paste:
Entra value Clevera field Microsoft Entra Identifier IdP Entity ID Login URL SSO sign-in URL Logout URL Logout URL (optional) The contents of Certificate (Base64) X.509 certificate Assign people
In Users and groups, click Add user/group and add the people or groups who should use Clevera.
Then finish in Clevera: domains and roles.
Connect with OpenID Connect
Register the app
In Clevera's setup dialog, set Protocol to OpenID Connect and copy the Redirect URI (callback URL) from the grey box. In Entra, go to App registrations and click New registration. Name it
Clevera, choose Accounts in this organizational directory only (Single tenant), and under Redirect URI choose Web and pastehttps://app.clevera.ai/sso/oidc/callback. Click Register.Copy the IDs
On the app's Overview, copy the Application (client) ID and the Directory (tenant) ID.
Create a client secret
Open Certificates & secrets, click New client secret, choose an expiry and click Add. Copy the secret's Value straight away (not the Secret ID); Entra shows it only once.
Add the email claim
Open Token configuration, click Add optional claim, choose ID, tick email and click Add. Accept the prompt to add the Microsoft Graph email permission. Without it, Clevera falls back to the sign-in name (
preferred_username), which works only when that is the person's email.Fill in Clevera
In Clevera, click Continue and enter:
Clevera field Value Client ID Application (client) ID Client secret The secret's Value Discovery URL https://login.microsoftonline.com/your Directory (tenant) ID/v2.0/.well-known/openid-configurationUse your tenant ID in the URL, not
commonororganizations: Clevera checks the issuer, and those shared URLs don't match it.Limit who can sign in (optional)
By default, anyone in your tenant can use the app. To limit it, open Enterprise applications → Clevera → Properties, set Assignment required? to Yes, and add people or groups in Users and groups.
Finish in Clevera
- On Domains & roles, add every email domain your people use, including any extra verified domains in your tenant. Choose Create accounts on first sign-in and the Default role for new SSO members.
- On Review, click Save configuration.
- Click Run test, switch on Enable SSO, and sign in as a test user in a private window, starting from the Clevera sign-in page.
- When it works for everyone, switch on Require SSO if you want SSO to be the only way in.
Members type their work email on the Clevera sign-in page and click Continue with Microsoft Entra ID (Azure AD).
Troubleshooting
| Problem | What to check |
|---|---|
| "SSO authentication failed…" after the Microsoft sign-in, with SAML | Signing Option is Sign SAML response and assertion; the certificate in Clevera is the active one; Identifier (Entity ID) matches Clevera exactly. |
| "SSO session expired. Please try again." after opening Clevera from My Apps | Expected: sign-in has to start on the Clevera sign-in page. |
| Microsoft says the reply URL doesn't match | Reply URL (SAML) or the Web redirect URI (OIDC) must be exactly the Clevera value. |
| Microsoft says the user isn't assigned | Add them in Users and groups, or set Assignment required? to No. |
| "SSO authentication failed…" with OIDC | The discovery URL uses your tenant ID; the secret is the Value, not the ID, and hasn't expired; the person has an email address. |
| "Your email domain is not authorized for this team's SSO." | Their email domain isn't in Allowed email domains. Add it in Clevera. |
More messages: Fix SSO sign-in problems.